

SSH
Reads SSH event types such as ssh_failed-auth, with usernames from target_user. These fields come from CrowdSec’s sshd parser. The integration also accepts older ssh_user metadata.
Evidence
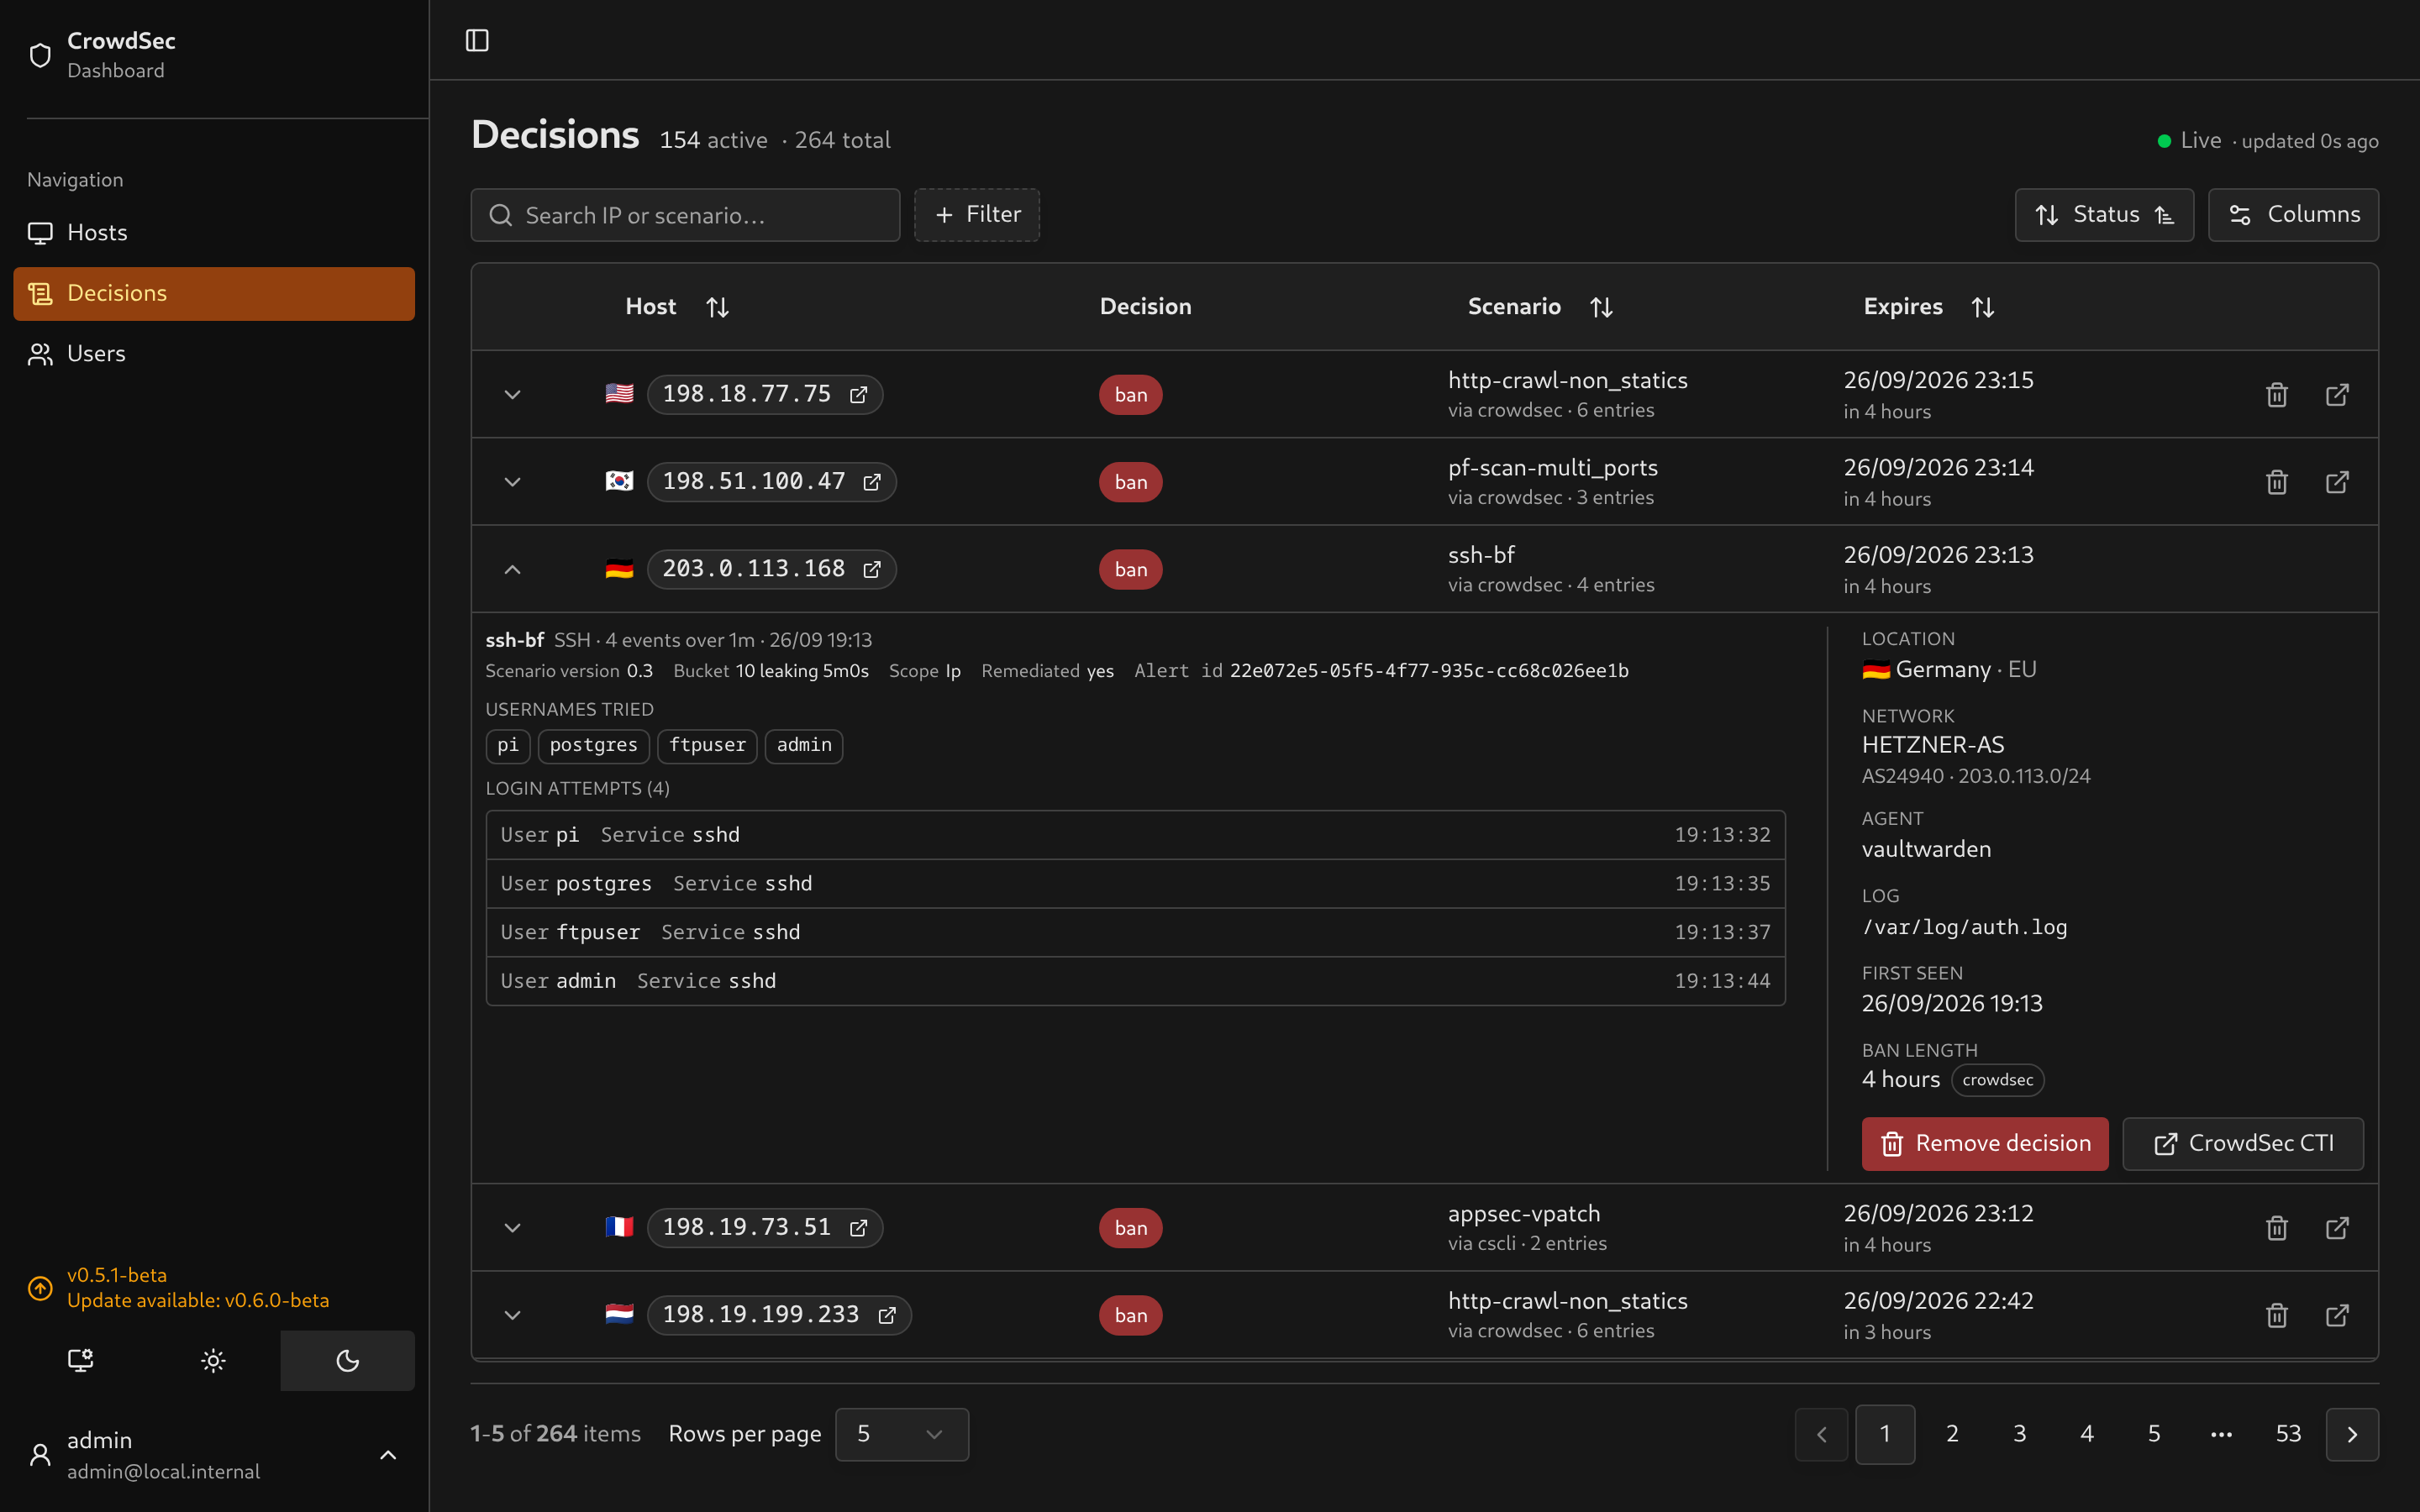
Section titled “Evidence”Usernames appear as chips, followed by each retained attempt’s username, service and time.
 |
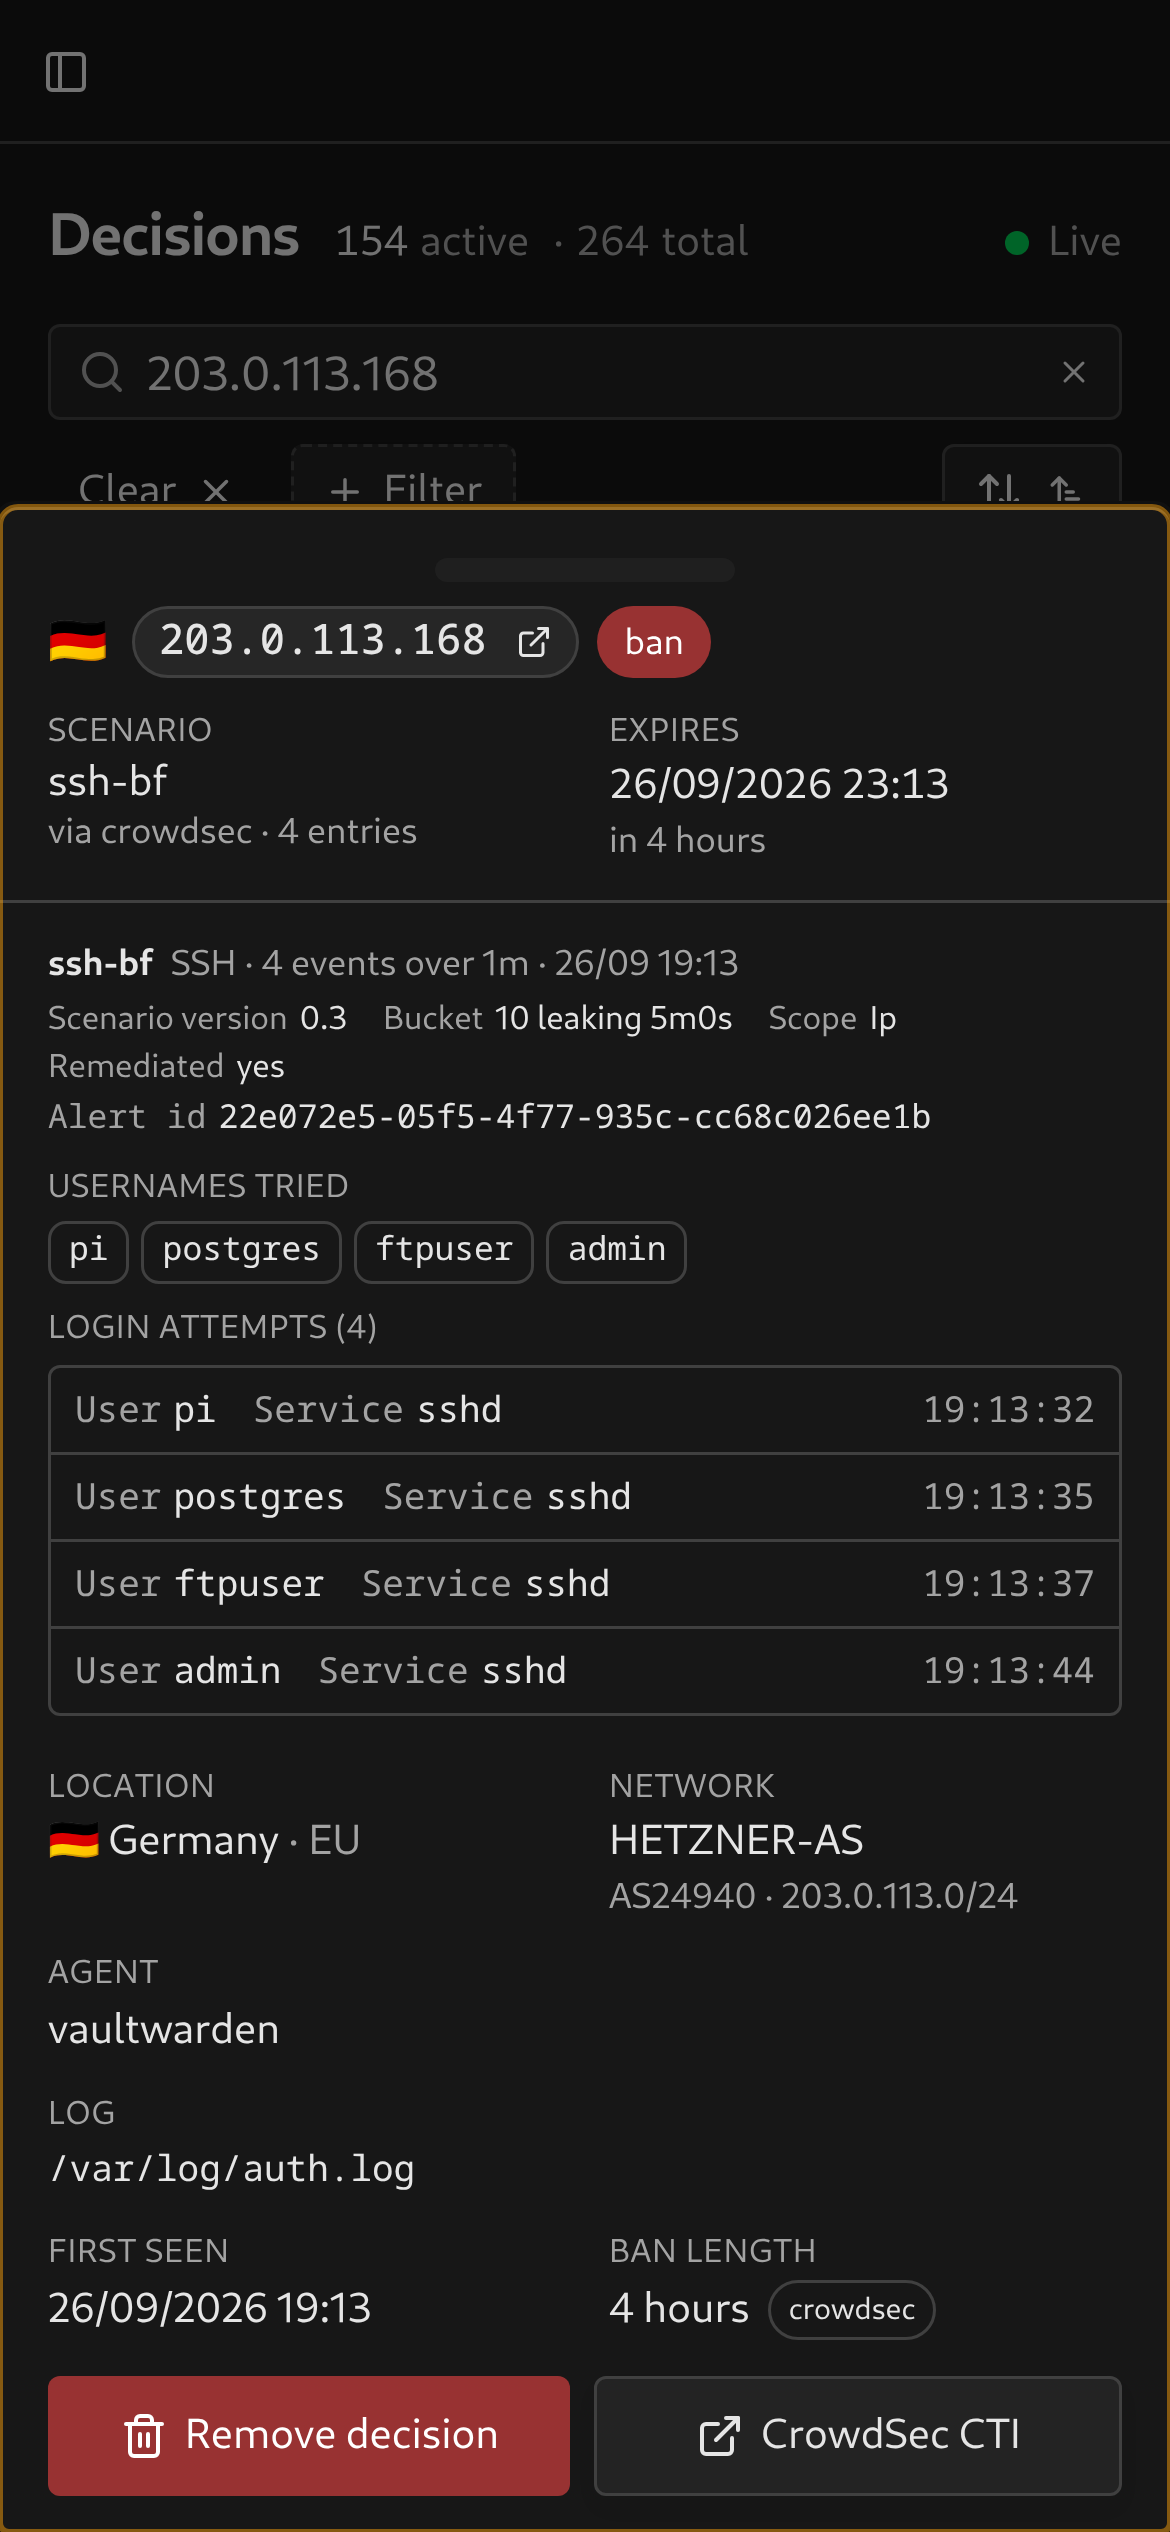 |
The username list combines alert aggregates with retained events. It can contain more names than the attempt list when CrowdSec has kept only part of the event history.
Configure CrowdSec to collect sshd logs and give the dashboard watcher credentials. Tests use upstream field definitions; a captured SSH alert is still needed to validate the complete integration. If you can provide one, open an issue with a sample alert.